

A Machine SBOM and Vulnerability Report lists the digital components inside one machine line, such as PLCs, HMIs, drives, gateways and industrial PCs, and the published vulnerabilities that affect them, built from the electrical component list you already have. It costs $1,500 for up to 100 components or $2,500 for 101 to 300. We never connect to your machines.
SoftWSP covers the whole loop for the software you own: scan, AI-assisted fix, re-scan as proof, and monitoring of machines you have sold. Findings cite their evidence, and MCP access for your own AI agents is coming. Your automation team is good at electrics, mechanics and PLC programming. Security questions from buyers and regulators are a different skill, and most machine builders do not have a security team. We fill that gap, starting from a list you already have.
At a glance
$1,500 for up to 100 components, $2,500 for 101–300
Delivered once we have a usable component list
Built from your existing component list — we never connect to your machines
Delivered remotely, worldwide
The problem
From January 2027, the EU Machinery Regulation 2023/1230 applies. It asks that machines sold in the EU be protected against corruption, including through their software and network connections. The EU Cyber Resilience Act adds vulnerability handling and an SBOM for products with digital elements. Large plant owners increasingly write IEC 62443 into their purchase contracts, and send suppliers security questionnaires.
A typical machine contains parts from many vendors: a PLC from one, an HMI from another, drives, a gateway, an industrial PC. Each has its own firmware and its own list of published vulnerabilities. Few builders can say what the whole machine contains, and fewer can say what is known to be wrong with it. Machines then stay in service for ten to twenty years, often with a remote access tool that nobody reviews.

How it works
You send the component list for one machine line. We identify each component and match it to published advisories. An engineer reviews the result and writes the report. You receive the report once it is ready, and we go through it together.
What do you need to prepare?
- The component list of one machine line: manufacturer, model, and firmware where known. Photos of device labels also help.
- One engineer who can answer a few questions by email or call.
What we do
Starting from the electrical bill of materials for one machine line, we work out:
Which digital components are inside
PLC, HMI, drives, gateways and industrial PC, with model and firmware.
Which published vulnerabilities affect them
We use CISA ICS advisories, vendor PSIRT notices and the CVE database.
What to do first
Items are ranked by what attackers actually exploit today, with the official fix or a mitigation.
Where you stand
An indicative matrix against the Machinery Regulation, the Cyber Resilience Act and IEC 62443-4-2.
Also available
Beyond the first report, we can also:
- Analyse software you wrote yourself, such as a Linux gateway, an HMI application or a cloud connector, which you own and can patch.
- Review PLC and HMI project files you export, for weak passwords, unnecessary services and unencrypted protocols.
- Design a safer remote service setup with strong authentication, approved sessions and logging.
- Prepare draft technical documentation and answers to customer security questionnaires.
- Monitor the components in machines you have already sold and alert you when a new vulnerability appears.
What you receive
- A Machine SBOM and Vulnerability Report for one machine line, in plain language for management and in detail for engineers.
- An indicative readiness matrix for the regulations above.
- A short call with our engineer to walk through the report.
See a sample report
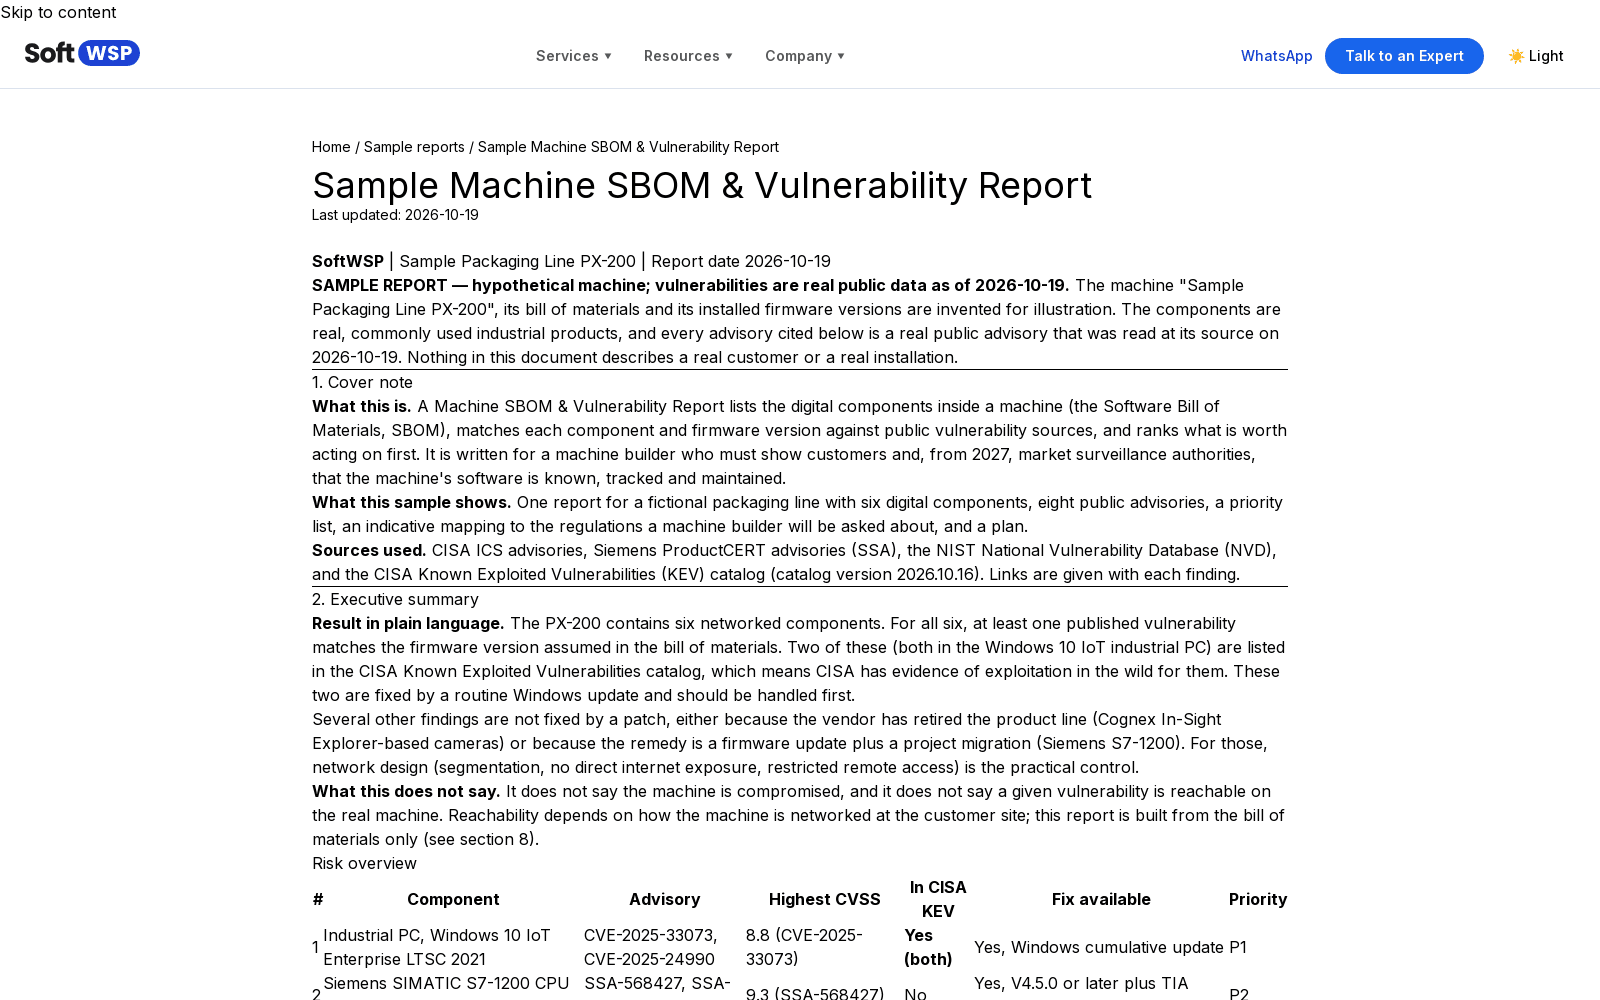
Sample Machine SBOM & Vulnerability Report
Scope and responsibilities
The report is based on the information you share. It does not test your machine and it is not a certification. We do not patch the firmware of third-party PLCs, robots or CNC controllers; we show you the vendor's fix or a mitigation. You stay in charge of decisions about your machines and of your compliance filings. Where a fix involves changing a running machine, your own engineers decide and carry it out under your safety procedures.
Pricing
Machine SBOM & Vulnerability Report
$1,500
1 machine line, ≤ 100 components
Join the Design Partner programmeMachine SBOM & Vulnerability Report
$2,500
1 machine line, 101–300 components
Join the Design Partner programmeFrequently asked questions
What do you need to start?
The electrical component list of one machine line: manufacturer, model and firmware version where known. A spreadsheet is enough.
Do you test our machines?
No. The report is based on the information you share. We do not connect to or test your machines.
Can you patch our PLC or robot firmware?
No. That firmware belongs to the component vendor and only the vendor can fix it. We point you to the official fix or to a mitigation. We can work on software that you own, such as a gateway or a PC application.
Is this a certification for the Machinery Regulation?
No. The matrix maps your components against the EU Machinery Regulation (EU) 2023/1230 and, where relevant, the Cyber Resilience Act (Regulation (EU) 2024/2847), but it is indicative and not a notified body's assessment. You remain responsible for decisions about your machines and for your compliance file.
How long does it take?
It depends on the size and clarity of your component list. Once we have a usable list for one machine line, we agree a delivery date with you before starting the work.
Can you help with remote service access?
Yes. Many builders service machines with remote tools set up years ago. We can review that setup and propose a safer design.
Can SoftWSP deliver a Machine SBOM report to a company in my country?
Yes. A Machine SBOM report is delivered remotely, worldwide: you send the inputs over an encrypted channel and we do the work from our side. Netbase JSC, the company behind SoftWSP, has worked with clients in 80 countries.
Do you work with companies in my industry?
Yes, if you build machines that contain PLCs, HMIs, drives, gateways or industrial PCs: packaging, food processing, plastics, printing, textile, woodworking and other automated lines sold into the EU or to large plant owners.
How do I pay for a Machine SBOM report?
Contracts and invoices are issued by the company, Netbase JSC. You pay by bank transfer to the company account or by PayPal Business. Unless the order says otherwise, invoices are payable within 15 days.
Who do I talk to about a Machine SBOM report?
Huy Nguyen (David), CEO of Netbase JSC, by WhatsApp at +84 937 869 689 (wa.me/84937869689) or by e-mail at [email protected].