Rows of illuminated server racks in a data center server room

AI-native security

AI-native security for devices, firmware and machines, from scan to proven fix

SoftWSP is an AI-native security service from Netbase JSC for device makers, machine builders and plants. We analyse firmware, machine component lists and passive shop-floor network recordings, report every finding with its evidence, help fix what you own, re-scan to prove the fix and keep monitoring. Work is remote and worldwide.

Last updated:

A Netbase JSC company

  • FoundedSince 2012
  • ReachClients in around 80 countries
  • Delivery modelRemote, worldwide

Facts of Netbase JSC as of . About the company

Services

Who we help

Device makers and brands, machine builders, plant and grid operators, and the product security teams that answer for them.

Guides by topic

Why SoftWSP

The full loop

Scan, AI-assisted fix, re-scan proof and monitoring, for firmware, in one service. Most tools in this field stop at the report.

Built for the regulation wave

Vulnerability-reporting duties under the EU Cyber Resilience Act apply from September 2026. The Machinery Regulation 2023/1230 applies from January 2027.

AI-native

AI drafts every finding with the evidence behind it, and an engineer reviews it before it reaches you.

New risks covered early

AI models and API keys embedded in firmware, MCP servers, and AI-enabled machines.

Remote-first, worldwide

You do not need to host us. Your engineer follows our guide and we do the rest.

Evidence, not promises

We report only what the evidence shows. No "100% secure" claims: every report states what it covers and what it does not.

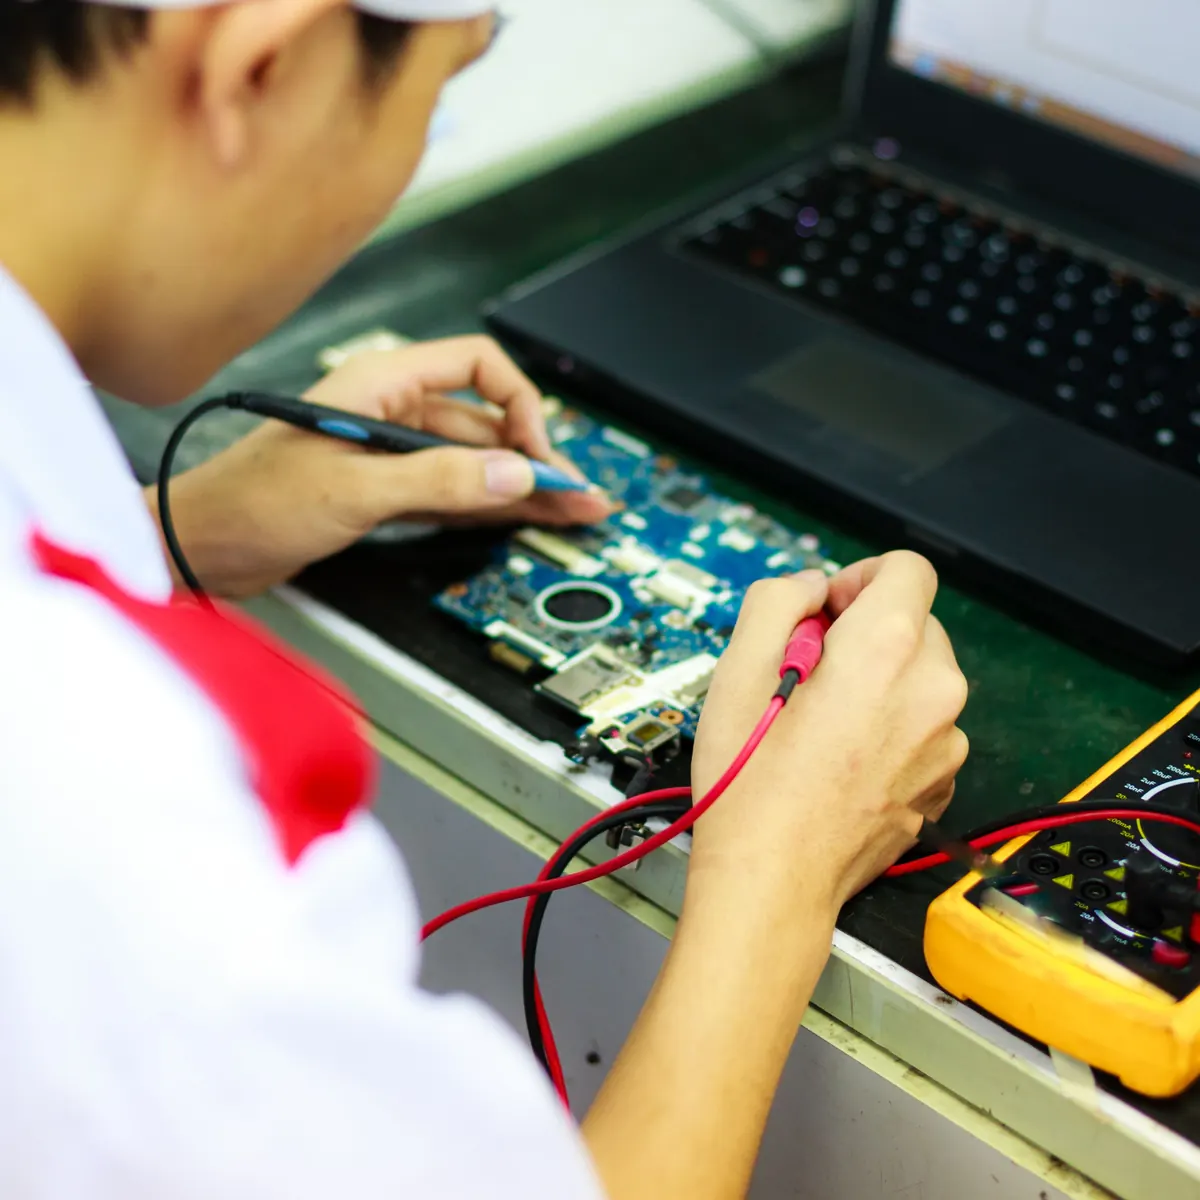
An engineer probes a circuit board with multimeter test leads at a workbench, next to an open laptop and a digital multimeter.

One loop, from scan to proven fix

Most security tools stop at the report. SoftWSP carries each finding through four steps, then starts again.

  1. 1. Scan

    We unpack your firmware, read a machine component list or a passive network recording, and match every component against NVD, CISA KEV and FIRST EPSS.

  2. 2. AI-assisted fix

    For firmware you own, AI prepares, builds and tests the patch, and an engineer reviews it before it reaches you.

  3. 3. Re-scan proof

    We scan the fixed build again, so your release manager signs off with a scan that shows the issue is gone.

  4. 4. Monitoring

    When a new vulnerability appears in a component you have shipped, you hear about it, ranked by how likely it is to be exploited.

See the evidence

Our process

Upload

You send a firmware file, a component list or a network recording, under a confidentiality agreement and over an encrypted channel.

Analysis

Our engine unpacks and inspects what you sent, then matches each component against public vulnerability sources such as the CVE database and CISA advisories.

Report

You receive a summary for management and a detailed version for engineers, with the evidence behind every finding.

Fix

For firmware you own, AI-assisted engineering prepares, builds and tests patches, then we scan again to show the result.

Monitor

When a new vulnerability appears in a component you have shipped, you hear about it, ranked by how likely it is to be exploited.

Client reviews of Netbase JSC

SoftWSP is delivered by Netbase JSC. These reviews are of Netbase JSC and its CMSmart products, quoted word for word as published on netbasejsc.com.

Client reviews of Netbase JSC

Sam Coldwell

United Kingdom

“We've been using the NB designer over the last few years and had nothing but rave reviews from customers who use it. We've also received excellent and timely support from the team at Netbase.”

5 out of 5 starsTrustpilot review, via netbasejsc.com · retrieved

Client reviews of Netbase JSC

Mapi Rodriguez

Spain

“Their commitment to meeting my needs promptly is commendable, and their patience in resolving issues sets them apart.”

5 out of 5 starsTrustpilot review, via netbasejsc.com · retrieved

Client reviews of Netbase JSC

Jun

United States

“From start to finish, the experience was exceptional, and I am thrilled to share my positive review about their outstanding services.”

5 out of 5 starsTrustpilot review, via netbasejsc.com · retrieved

Technologies and data sources

What SoftWSP runs, from upload to report

Firmware and SBOM

  • unblob

    Unpacks the filesystem of a raw firmware image

  • Syft

    Lists the software components in the unpacked image

  • CycloneDX

    The open format each SBOM is written in

  • SPDX

    The other open SBOM format, read by the free SBOM viewer and SBOM diff tools

Shop-floor network recordings

  • Zeek

    Reads a passive network recording into a connection log

  • ICSNPP

    Decodes industrial protocols such as Modbus and S7comm

AI and platform

  • Claude (Anthropic)

    Drafts advisory and report text from cited evidence, reviewed by an engineer

  • PostgreSQL

    Stores the knowledge graph and each organisation's data, isolated per tenant

  • S3-compatible object storage

    Holds uploaded files and finished reports

  • FastAPI

    Serves the platform API behind the dashboard and reports

Technologies Netbase JSC works with

The platforms, languages and clouds Netbase JSC builds with.

  • WooCommerce
  • Shopify
  • PrestaShop
  • Shopware
  • Odoo
  • Laravel
  • Symfony
  • WordPress
  • PHP
  • React Native
  • Python
  • Google Cloud
  • DigitalOcean
  • Cloudflare

Source: Netbase JSC technology registry, attested 2026-09-15.

Names are trademarks of their respective owners, used only to name a technology or data source (nominative use). No endorsement or partnership is implied.

Enterprise

Security for a whole product range or several plants

For enterprises and their supply chains: one scope, one team and one contract for every device, machine and site you need covered.

Your whole range in one scope

Several products, firmware versions or sites in one engagement, so your security lead sees one picture instead of a stack of reports.

API access

API keys for your organisation, so your own tools can send inputs and read findings and reports without anyone copying files.

Confidentiality first

Work starts under a confidentiality agreement, and every file travels over an encrypted channel.

One engineer team

The same engineers across every product and site, so nobody has to explain your setup twice.

SoftWSP closes the loop that most security tools leave open. We scan firmware, machine components and plant networks, use AI to propose and prepare the fix, scan again to prove the result, and keep monitoring after release. Every AI-written finding cites its evidence, and an engineer reviews it before it reaches you.

Who does SoftWSP help?

  • Device makers and brands selling cameras, routers, access control, chargers, inverters and other connected products into the EU, UK and US, including brands that hold only a binary firmware file from an ODM.
  • Machine builders who ship PLCs, HMIs, drives and gateways inside a machine, and who now get security questions from buyers and regulators.
  • Plants and factories that want to know what is on the shop-floor network and who can connect to it, without installing sensors or touching running machines.

Three offers

Device firmware security. We unpack your firmware, build the software bill of materials, match it to published vulnerabilities and tell you what to fix first. Where you hold the source code, we make the fix, test it and scan again. Read more about device firmware security.

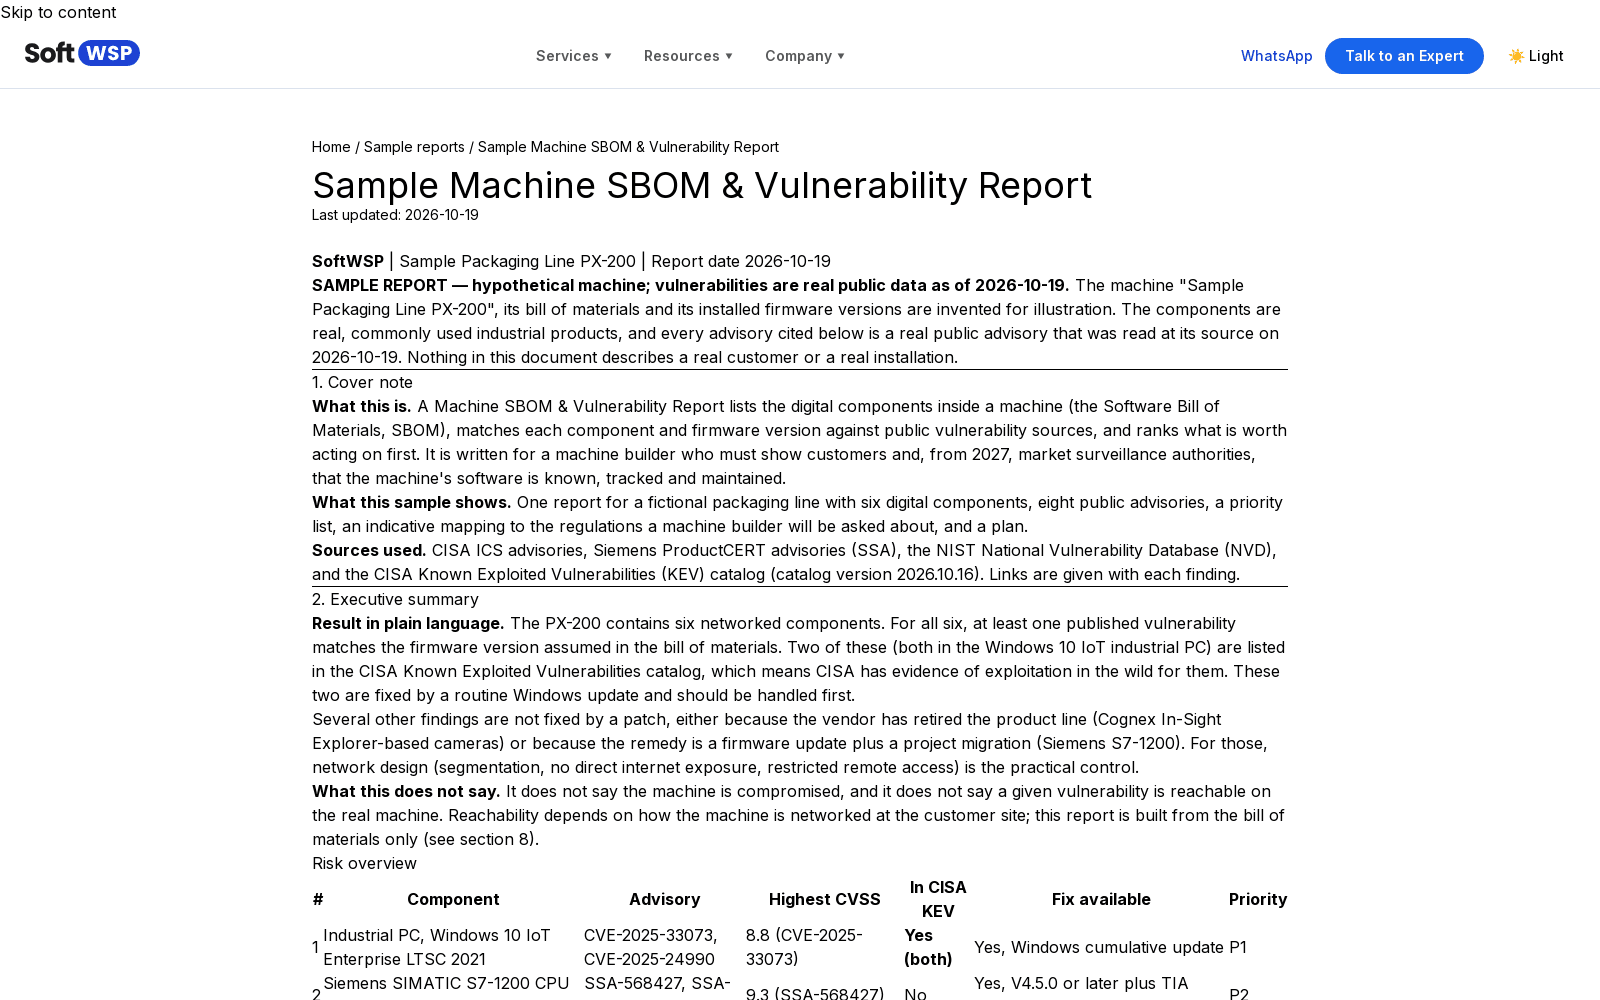
Machine builder reports. From the electrical component list of one machine line, we produce a Machine SBOM and Vulnerability Report that shows which digital components are inside and which published vulnerabilities affect them. Read more about Machine SBOM reports.

OT Snapshot for plants. Your engineer records 24 to 72 hours of shop-floor traffic from a mirror port. We turn the file into a device inventory, a vulnerability list and a map of remote access. Read more about OT Snapshot.

For device makers who need a way to receive and handle vulnerability reports, we also run a PSIRT service.

How it works

  1. Upload. You send a firmware file, a component list or a network recording, under a confidentiality agreement and over an encrypted channel.
  2. Analysis. Our engine unpacks and inspects what you sent, then matches each component it finds against public vulnerability sources such as the CVE database and CISA advisories to show which published vulnerabilities affect it.
  3. Report. You receive a summary for management and a detailed version for engineers, with the evidence behind every finding.
  4. Fix. For firmware you own, AI-assisted engineering prepares patches, builds them and tests them in an emulated environment, then we scan again to show the result. Final testing happens on real hardware in a lab that you set up and we operate remotely.
  5. Monitor. When a new vulnerability appears in a component you have shipped, you hear about it, ranked by how likely it is to be exploited.

What makes SoftWSP different

  • The full loop. Scan, AI-assisted fix, re-scan proof and monitoring, for firmware, in one service. Most tools in this field stop at the report.
  • Built for the regulation wave that is already here. Vulnerability-reporting duties under the EU Cyber Resilience Act apply from September 2026. The RED delegated act and EN 18031 have applied to radio equipment since August 2025. The Machinery Regulation 2023/1230 applies from January 2027.
  • AI-native. AI drafts every finding with the evidence behind it, and an engineer reviews it before it reaches you.
  • New risks covered early. AI models and API keys embedded in firmware (an AI bill of materials), MCP servers, and AI-enabled machines.
  • Remote-first, worldwide. You do not need to host us. Your engineer follows our guide and we do the rest.
  • Evidence, not promises. We report only what the evidence shows. No "100% secure" claims: every report states what it covers and what it does not.

What is changing in device security

Four shifts are reshaping what manufacturers are expected to show. Our guides explain each one.

  • Reporting duties are live. Manufacturers selling in the EU now need a working way to receive, assess and report vulnerabilities. See the Cyber Resilience Act guide.
  • Machines are becoming regulated digital products. From January 2027 security enters machine conformity. See the Machinery Regulation guide.
  • Radio equipment has a security baseline. Wi-Fi and Bluetooth products face EN 18031. See the EN 18031 guide.
  • Firmware is now an SBOM question. Buyers ask what is inside a binary. See the firmware SBOM guide.

AI adds a fifth: firmware that ships with models, API keys and agent interfaces that older checklists never anticipated. Please check the current text of each rule for your own product.

Start with the Design Partner programme

The first five device makers or machine builders and the first five plants receive their first report free of charge, in return for feedback on the report. If you have a firmware file, a machine component list or a network recording you would like examined, we would like to hear from you.

Join the Design Partner programme

Frequently asked questions

Who is SoftWSP for?

Device makers and brands selling connected products into the EU, UK and US, machine builders, and manufacturing plants that need to know what is on their shop-floor network.

Do you replace a certification body?

No. Our reports support your compliance work. Under the EU Cyber Resilience Act (Regulation (EU) 2024/2847), they are not a certificate, and responsibility for compliance stays with the manufacturer or importer.

Do you work on site?

Almost all work is remote, worldwide. Your engineer prepares the inputs or a test lab on your premises, and we do the analysis and engineering from our side.

Can our own AI agents use SoftWSP?

SoftWSP already works with AI on its side: AI drafts each finding with the evidence behind it, and an engineer reviews it before it reaches you. If you want your own AI agents or developer tools connected to your SoftWSP results, Netbase JSC, the company behind SoftWSP, scopes and builds that integration as a custom service.

Can SoftWSP deliver a SoftWSP service to a company in my country?

Yes. A SoftWSP service is delivered remotely, worldwide: you send the inputs over an encrypted channel and we do the work from our side. Netbase JSC, the company behind SoftWSP, has worked with clients in 80 countries.

Do you work with companies in my industry?

Device makers and brands of connected products, machine builders, and manufacturing plants of any industry. If your product or plant runs firmware, PLCs or connected devices, the services apply.

How do I pay for a SoftWSP service?

Contracts and invoices are issued by the company, Netbase JSC. You pay by bank transfer to the company account or by PayPal Business. Unless the order says otherwise, invoices are payable within 15 days.

Who do I talk to about a SoftWSP service?

Huy Nguyen (David), CEO of Netbase JSC, by WhatsApp at +84 937 869 689 (wa.me/84937869689) or by e-mail at [email protected].

Start with the Design Partner programme
The first five device makers or machine builders and the first five plants receive their first report free of charge, in return for feedback on the report.