

Cybellum, Binarly and NetRise all analyse binary firmware without source code, but they lean in different directions: Cybellum towards product security and compliance management for regulated device makers, Binarly towards deep binary and supply-chain analysis with exploitation scoring, and NetRise towards visibility into compiled code and third-party firmware for both builders and buyers. None of the three publishes a price.
Disclosure. This page is published by SoftWSP, a brand of Netbase JSC, founded in 2012. SoftWSP appears in the table as a fourth option. Facts about the three vendors come from their own pages, read on 26 October 2026.
Side-by-side
| Cybellum | Binarly | NetRise | SoftWSP | |
|---|---|---|---|---|
| What it is | Product security platform | Transparency Platform for binaries | Turbine visibility platform | Engineer-delivered service |
| Binary firmware, no source | Yes | Yes | Yes | Yes |
| SBOM | Merges SPDX and CycloneDX | CycloneDX, SPDX, CBOM | Not publicly listed | Included in report |
| Prioritisation | EPSS, AI triage assistant | Reachability, EPSS, exploitation maturity | Reachability, EPSS, CISA KEV | CVE, CISA KEV, FIRST EPSS |
| VEX | Yes, plus CSAF | CycloneDX VEX, OpenVEX | Not publicly listed | Free VEX generator (CycloneDX, CSAF) |
| CRA | Evidence templates, regulator reports | No dedicated CRA page listed | Readiness reports, sample CRA reports | Drafts Art. 14 reports (PSIRT service) |
| Fix help | Explains how to fix and mitigate | Not publicly listed | Helps identify and prioritise | Prepares, builds and tests fixes when you hold the source |
| OT / industrial | Industrial page mentions OT networks | Not publicly listed | Lists xOT visibility | Separate OT Snapshot service |
| Delivery | Public cloud or own data centre | SaaS, on-prem, air-gapped | Not stated | Remote, worldwide |
| Target | Automotive, medical, industrial makers | Hardware OEMs, software vendors, enterprise buyers | Builders and buyers, critical infrastructure | Small and mid-size device makers |
| Price | Not publicly listed | Not publicly listed | Not publicly listed | Published price list: pricing |
Cybellum
Cybellum's platform covers SBOM management, vulnerability management and compliance management. It merges SBOMs in SPDX and CycloneDX, prioritises with EPSS and an AI triage assistant, and produces VEX and CSAF reports. For the Cyber Resilience Act it offers evidence templates and one-click regulator reports. It explains how to fix or mitigate findings without changing code. It runs in the public cloud or the customer's data centre, agentless.
Binarly
Binarly analyses compiled binaries without source. Its documentation lists CycloneDX and SPDX SBOM export, a cryptographic bill of materials, and VEX export in CycloneDX and OpenVEX. Version 3.0 added real-time threat intelligence and an exploitation-maturity score on top of reachability and EPSS. It can run as SaaS, on-premises or air-gapped. On 26 October 2026, Binarly's public site had no page dedicated to CRA.
NetRise
NetRise Turbine analyses compiled code and third-party firmware and narrows vulnerabilities through reachability, EPSS and CISA KEV. Its CRA page offers release-build SBOMs, vulnerability-handling evidence and sample CRA reports, and it lists visibility across OT and IoT. Dragos announced the acquisition of NetRise on 21 September 2026.
Where does SoftWSP fit?
SoftWSP is a different kind of option: an engineer-delivered service for device makers without a security team. We analyse the firmware, an engineer reviews every finding, and where you hold the source we prepare and test the fix and scan again. Fixed-scope report prices are on the pricing page. VEX documents in CycloneDX and CSAF are produced with the free VEX generator; our CSAF and VEX guide explains both formats. See device firmware security.
Which one fits your team?
Choose Cybellum, Binarly or NetRise if
- your own team runs the analysis on many product lines every release, in a self-service platform
- you need VEX managed across a product portfolio (Cybellum, Binarly)
- you need compliance evidence (Cybellum), compiled-binary depth (Binarly) or visibility into devices you buy as well as build (NetRise)
Choose SoftWSP if
- you have no security team and want every finding reviewed by an engineer and explained
- you hold the source code and want the fix prepared, built and tested, then proved with a second scan
- you want a published price list before a sales call, or to start with one firmware version
How does SoftWSP work?
ScanWe unpack the binary firmware image, even without source code, build its SBOM and match every component to the CVE database, CISA KEV and FIRST EPSS. An engineer reviews every AI-written finding before you receive the report. AI-assisted fixWhere you hold the source code, we agree the scope in writing, then patch, build and test the firmware in an emulated environment. AI-written work cites its evidence and an engineer reviews it. Re-scan as proofWe scan the fixed build again, so the before-and-after result shows the vulnerability is gone. You sign and release the firmware with your own keys. MonitorWhen a new vulnerability affects a component in firmware you have already sold, we alert you, ranked by how likely it is to be exploited.
Details: device firmware security, PSIRT service, pricing.
What does a SoftWSP report look like?
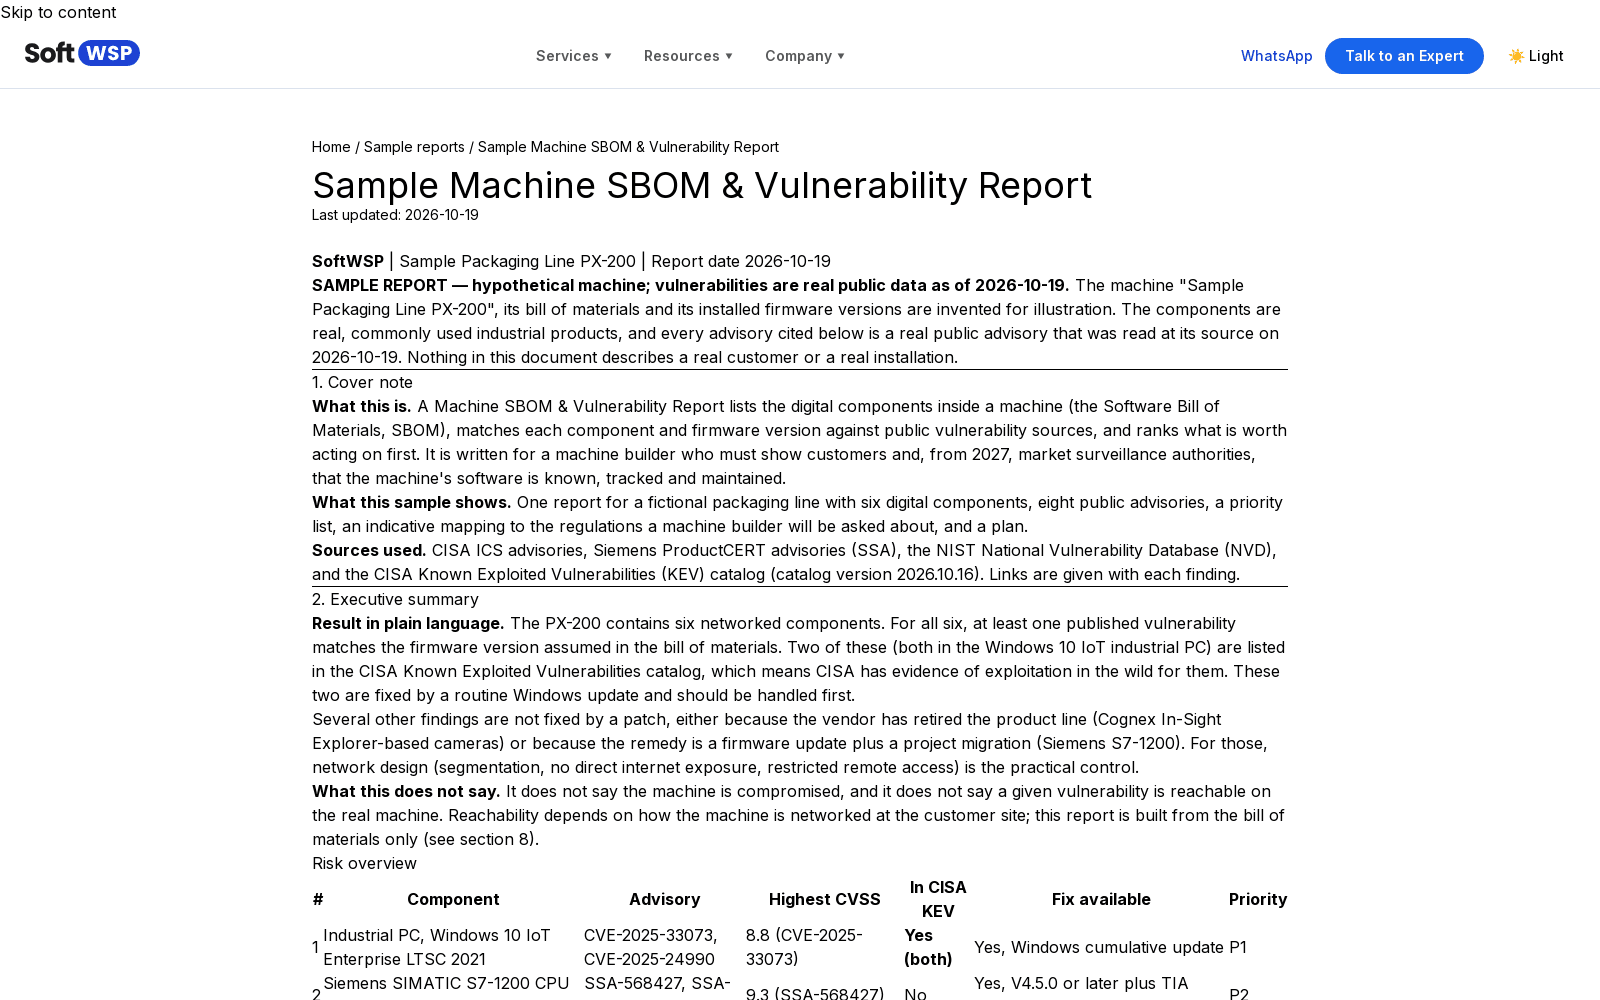
Sample Machine SBOM & Vulnerability Report: sample report (hypothetical machine)
SoftWSP's sample deliverable, for reference: a component SBOM, real public vulnerabilities ranked by priority with the source of each one, an indicative compliance mapping and a plan of recommended actions. The other tools on this page were not assessed against it.
Frequently asked questions
What is the difference between Cybellum, Binarly and NetRise?
All three analyse binary firmware or compiled code. Cybellum focuses on product security and compliance management for automotive, medical and industrial makers; Binarly's own documentation describes its goal as "ground-truth visibility into compiled software and firmware... without source code access," with reachability and exploitation-maturity scoring; NetRise on visibility into compiled code and third-party firmware for builders and buyers, now as part of Dragos.
Which one is best for EU Cyber Resilience Act work?
On their own pages, Cybellum offers CRA evidence templates and regulator reports, and NetRise's CRA page says it helps teams "prepare for EU CRA obligations with evidence based on binary artifacts rather than source code." We found no dedicated CRA feature page for Binarly. None of them states that it files Article 14 reports.
Do Cybellum, Binarly and NetRise support VEX?
Cybellum issues VEX and CSAF reports, and Binarly exports CycloneDX VEX and OpenVEX. The NetRise pages we read on 26 October 2026 list no VEX support. SoftWSP's free VEX generator creates CycloneDX VEX and CSAF VEX documents in the browser.
How much do Cybellum, Binarly and NetRise cost?
None of the three lists a price on its website (read 26 October 2026); all offer demos on request. For comparison, SoftWSP publishes a price list for its fixed-scope reports at softwsp.com/pricing/.
What happened to NetRise?
Dragos announced on 21 September 2026 that it acquired runZero and NetRise. Check the current Dragos and NetRise pages for how the product is sold now.
Who wrote this comparison?
SoftWSP, built by Netbase JSC. SoftWSP is shown in the table as a fourth option. Facts about Cybellum, Binarly and NetRise come from their own websites and documentation, read on 26 October 2026.
Related reading
Sources
- Cybellum: platform, SBOM management, vulnerability management, compliance management (read 26 Oct 2026)
- Cybellum: industrial manufacturing (read 26 Oct 2026)
- Binarly documentation: why Binarly (read 26 Oct 2026)
- Binarly documentation: SBOM export (read 26 Oct 2026)
- Binarly documentation: VEX export (read 26 Oct 2026)
- Binarly: Transparency Platform v3.0 announcement (read 26 Oct 2026)
- NetRise Turbine (read 26 Oct 2026)
- NetRise: EU CRA compliance (read 26 Oct 2026)
- Dragos press release: Dragos acquires runZero and NetRise (read 26 Oct 2026)